Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalSoftware Engineering
DZone

Designing the Runtime Layer for Stateful AI Agents: Where Agent Substrate Fits

Introduction: The Layer Nobody Designs AI agents are evolving from simple prompt-response systems into stateful, long-running applications that can reason, execute tasks, and interact with external systems. Yet, most agent architectures are driven by models, tools, memory, and orchestration — not runtime infrastructure that can run agents reliably. Unlike traditional applications, stateful AI agents need execution context to run (and recover from failures), concurrent tasks, and the ability to r

ExternalCybersecurity
SecurityWeek

Sysdig Adds Runtime Security and Governance for AI Agents

Sysdig’s platform uses runtime visibility to track AI agent actions and block risky behavior before it reaches production systems. The post Sysdig Adds Runtime Security and Governance for AI Agents appeared first on SecurityWeek.

Application SecurityArtificial Intelligenceagentic AI
SecurityWeekRead original
External
The Hacker News

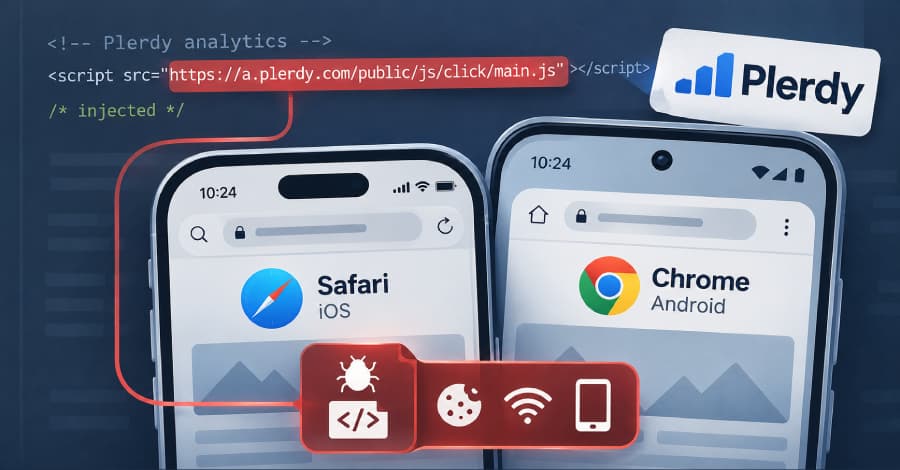
APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits

The Russia-linked threat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker. "The injected JavaScript code collects browser and device attributes," Sekoia researchers Amaury-Jacques Garçon and

The Hacker NewsRead original
ExternalCybersecurity
SecurityWeek

Barracuda ESG Authentication Bypass Flaw Opens Path to Root

An authentication bypass and a command injection flaw can be chained for root access on Barracuda’s Email Security Gateway appliances. The post Barracuda ESG Authentication Bypass Flaw Opens Path to Root appeared first on SecurityWeek.

Email SecurityVulnerabilitiesBarracuda
SecurityWeekRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.