Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalSoftware Engineering
DZone

Context Engineering: The Missing Piece in Agentic Systems

Context engineering is becoming essential as AI agents take on more software development work. An agent can plan, code, test, investigate incidents, trigger CI, and help deploy software. But none of that matters if it is operating without the right information. This is the main problem I keep seeing. We connect an LLM to a few tools, give it a good prompt, and expect magic. Then the agent has to figure out which service we mean, who owns it, what repository it belongs to, whether it is healthy,

ExternalCybersecurity
SecurityWeek

Comp AI Raises $34 Million for AI-Native Compliance and Security

The company plans to expand into continuous cybersecurity, offering security testing across applications and infrastructure. The post Comp AI Raises $34 Million for AI-Native Compliance and Security appeared first on SecurityWeek.

ComplianceCybersecurity FundingRisk Management
SecurityWeekRead original
ExternalTechnology Trends
The Verge Tech

Bose’s next open earbuds have more bass, more volume, and more battery life

Bose announced a new version of its Ultra Open Earbuds that helped kick off the industry trend of clip-on wireless earbuds nearly two-and-a-half years ago. The new Ultra Open Earbuds (2nd Gen) feature a subtle redesign with improved performance in both sound quality and battery life. They're also joined by a new cheaper alternative called the Bose Sport Open Earbuds designed to provide a more secure and stable fit during physical activities. The Bose Ultra Open Earbuds (2nd Gen) will be availabl

The Verge TechRead original
ExternalCybersecurity
SecurityWeek

ISC Patches 14 Vulnerabilities in BIND 9 Security Update

Attackers could exploit the flaws to increase resource usage, trigger an unexpected program exit, or terminate the named process. The post ISC Patches 14 Vulnerabilities in BIND 9 Security Update appeared first on SecurityWeek.

VulnerabilitiesBINDDNS
SecurityWeekRead original
External
The Hacker News

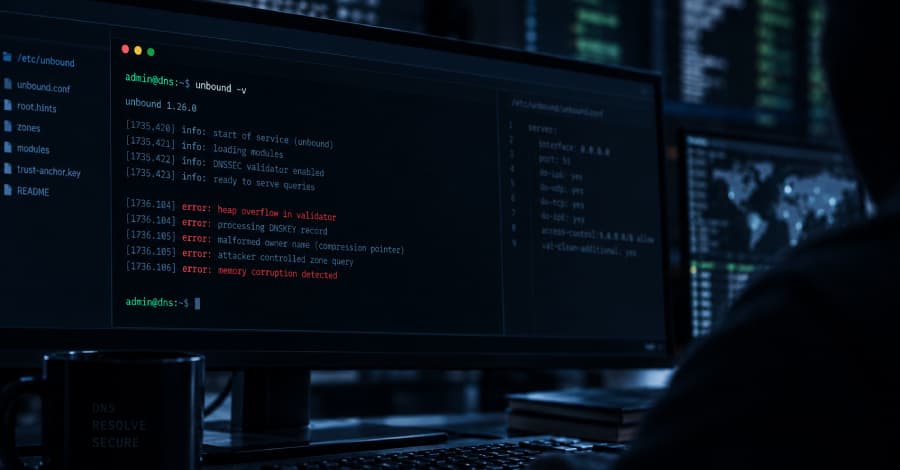
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone

Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday. An attacker who controls a malicious zone and queries a vulnerable resolver can trigger it, enabling remote code execution. Unbound 1.26.1, released the same day, fixes the bug, tracked as CVE-2026-81642, along with

The Hacker NewsRead original
ExternalCybersecurity
SecurityWeek

Ransomware Attacks on Manufacturers Surge as Supply Chain Risk Grows

Research shows attacks on manufacturers rose 40% in early 2026, as ransomware groups increasingly exploit the supply-chain disruption caused by operational shutdowns. The post Ransomware Attacks on Manufacturers Surge as Supply Chain Risk Grows appeared first on SecurityWeek.

ICS/OTRansomwareOT
SecurityWeekRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.