ExternalTechnology Trends
Hacker News
Mistral X Mozilla: Private, Multilingual AI Browsing
Comments
Hacker NewsRead original
Insights
Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.
From the engineering desk
Browse practical articles or follow the latest technology updates.
Subscribe via RSS →Curated links from external sources — not 360Softy original articles.
Comments
Google has released the September 2026 security patches to address 110 vulnerabilities affecting its Pixel devices, including one zero-day flaw actively exploited in targeted attacks. [...]
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. "This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and achieve remote code execution," Wordfence said. The WordPress security company said it has blocked over
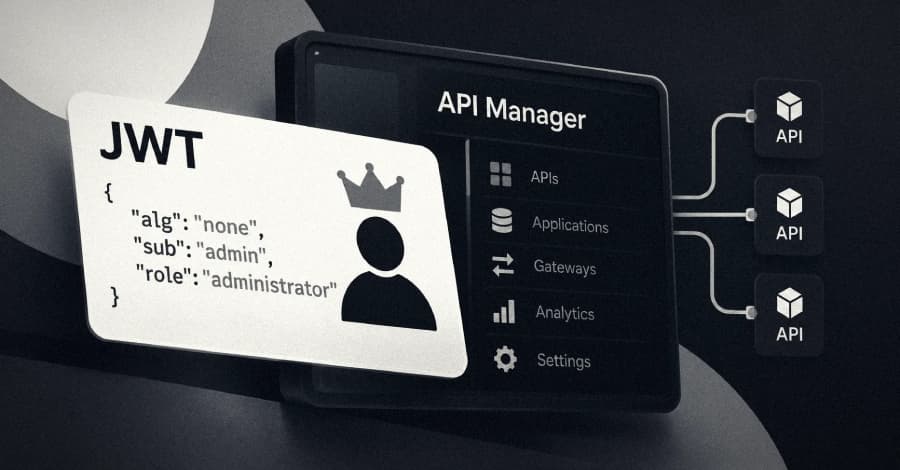
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktron Team has been credited with discovering and reporting the flaw. "JWT authentication
Adults first demonstrate tool use, then hand over the implements to their infants, who copy the behavior.
Laravel 13.32 adds a Mercure broadcast driver, Storage::copyToDisk() and moveToDisk(), enum support in queue pause/resume, and more. The post Mercure Broadcasting in Laravel 13.32 appeared first on Laravel News. Join the Laravel Newsletter to get Laravel articles like this directly in your inbox.
Article URL: https://security.apple.com/blog/apple-reference-image/ Comments URL: https://news.ycombinator.com/item?id=49721322 Points: 524 # Comments: 351
Let’s start with a conversation
An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.
Prefer email? [email protected]