Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalSoftware Engineering
GitHub Changelog

Safer pull_request_target defaults for GitHub Actions checkout

The pull_request_target event is one of the most commonly misused triggers in GitHub Actions, leading to vulnerabilities in workflows. Workflows triggered by pull_request_target run with the base repository’s GITHUB_TOKEN, secrets,… The post Safer pull_request_target defaults for GitHub Actions checkout appeared first on The GitHub Blog.

GitHub ChangelogRead original
ExternalSoftware Engineering
GitHub Changelog

Control who and what triggers GitHub Actions workflows

Workflow execution protections are now in public preview for GitHub Enterprise, organizations, and repositories. This new capability lets enterprise administrators define an allow list that controls who can trigger GitHub… The post Control who and what triggers GitHub Actions workflows appeared first on The GitHub Blog.

GitHub ChangelogRead original
ExternalSoftware Engineering
DZone

The Latency Tax That’s Hidden in Cloud-Native Systems (and the Hard Lessons I Learned to Minimize It)

Let’s be real, shall we? Do you remember the early days of our cloud-native promise? We dove in headfirst, building microservices by breaking apart monolithic applications and starting to deploy to the cloud with all sorts of containers. We had unlocked the secret of scaling and resiliency, it seemed. And we had! But wait... wasn’t it?   The first time I faced a real perplexing (remember these are my lessons learned, and I murdered more than a few prior to finding the right way) performance issu

ExternalMobile Development
Android Developers Blog

Android developer verification: Building a safer ecosystem together

Posted by Matthew Forsythe, Director Product Management, Android App Safety Last year, we introduced Android developer verification to strengthen ecosystem security and stop malicious actors from hiding behind anonymity to release harmful apps. Millions of apps have been registered since the verification launched in March, covering nearly all installs on Google Play and a large majority of installs from outside of Google Play. We appreciate the feedback and partnership from industry leaders,

Android Developers BlogRead original
External
The Hacker News

The Scripts on Your Checkout Page Are Now a PCI DSS Problem

An independent PCI assessor tested Reflectiz against the new PCI DSS rules. Here is the verdict: See the full QSA assessment here → When a customer types their card number into your checkout, their browser is running far more than your code. Analytics tags, a tag manager, a support widget, a payment iframe: a modern checkout loads dozens of third-party scripts, and any one of them can be turned

The Hacker NewsRead original
External
The Hacker News

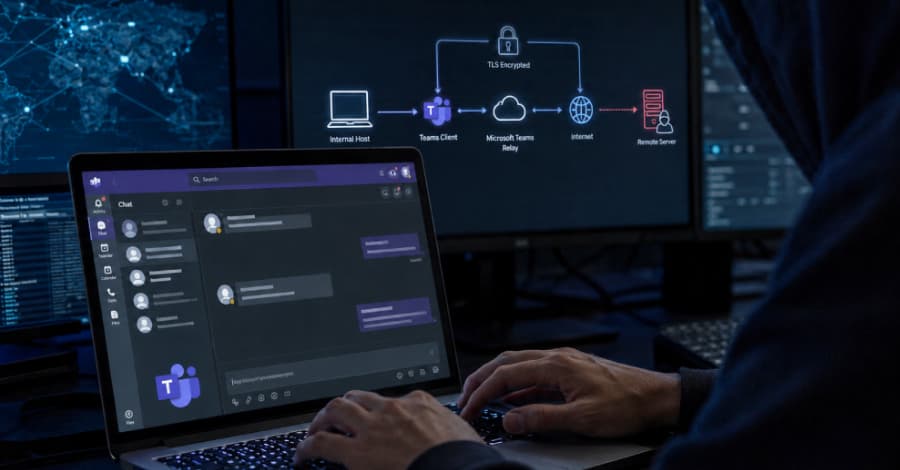
DragonForce Hackers Abuse Microsoft Teams Relays to Hide Backdoor.Turn C2 Traffic

Threat actors associated with the DragonForce ransomware have been observed using a custom Go-based remote access trojan (RAT) called Backdoor.Turn to conceal command-and-control (C2) traffic inside Microsoft Teams relay infrastructure. According to findings from Broadcom-owned Symantec and Carbon Black, the backdoor was deployed against a major U.S. services firm. The name of the company was

The Hacker NewsRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.