Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalCybersecurity
SecurityWeek

OpenAI Unveils GPT-5.6 Sol as Its Most Advanced Cybersecurity AI

The company says Sol matches competing systems like Mythos Preview while using only a third of the output tokens. The post OpenAI Unveils GPT-5.6 Sol as Its Most Advanced Cybersecurity AI appeared first on SecurityWeek.

Artificial IntelligenceAIFeatured
SecurityWeekRead original
External
The Hacker News

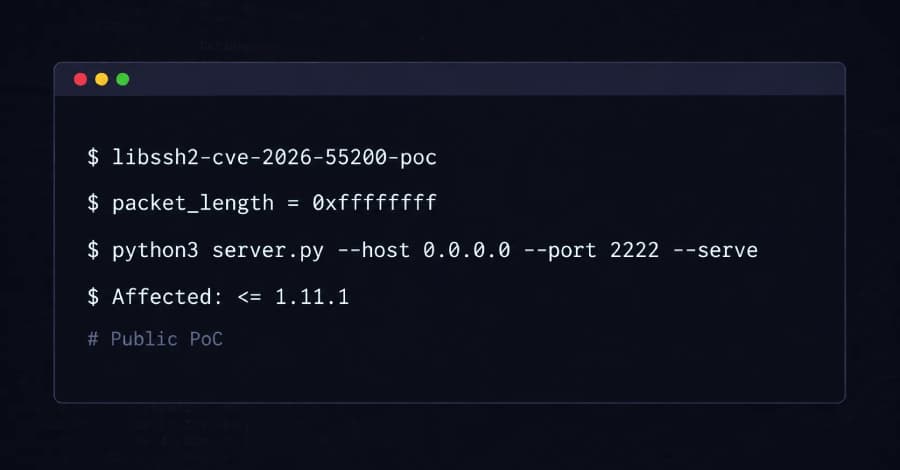
Public PoC Released for Critical libssh2 CVE-2026-55200 Client-Side SSH Flaw

A public proof-of-concept is now out for CVE-2026-55200, a critical flaw in libssh2 that lets a malicious or compromised SSH server trigger memory corruption on a connecting client, with possible code execution. No credentials, no user interaction. The bug affects every release up to and including 1.11.1 and carries a CVSS 4.0 score of 9.2. libssh2 is a client-side SSH library, not a server.

The Hacker NewsRead original
ExternalFrontend Development
Vercel Blog

Build realtime voice agents on AI Gateway

now supports audio/voice. You can add realtime voice, text to speech, and speech to text with the same calls you already use for text, image, and video, routed through AI Gateway alongside every other modality.AI Gateway Audio launches with models from and . Each call gets the same provider routing, observability, spend controls, and bring-your-own-key support you already use for your other models.OpenAIxAI These capabilities are in beta and available in 7.AI SDK Realtime, speech, and transcri

Vercel BlogRead original
External
The Hacker News

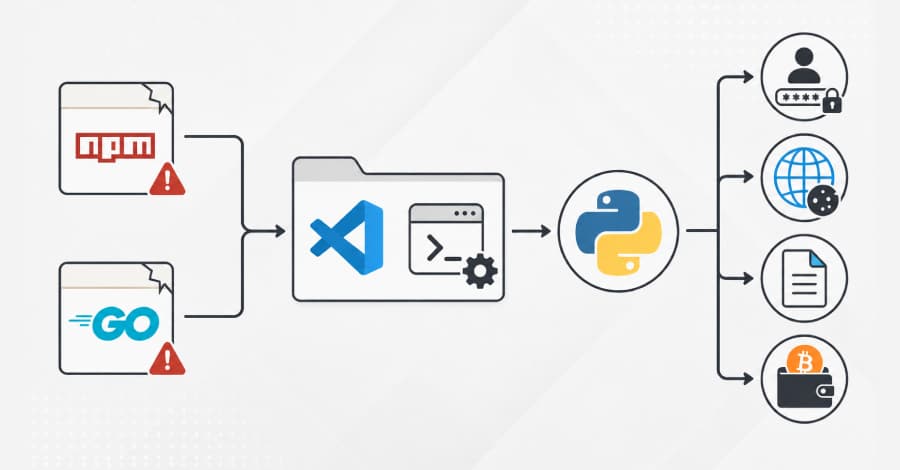
Hijacked npm and Go Packages Use VS Code Tasks to Deploy Python Infostealer

Cybersecurity researchers have uncovered two hijacked npm packages and a cluster of Go packages that are designed to deploy a Python-based information stealer on compromised Windows, Linux, and macOS hosts. "This attack avoids the most common npm execution paths through lifecycle scripts, perhaps in an attempt to remain 'compatible' with npm v12's security hardenings," JFrog said in a

The Hacker NewsRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.