Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalCybersecurity
SecurityWeek

SecurityWeek Launches Critical Impact Awards to Recognize Excellence in Industrial Cybersecurity

Independently judged and sponsor-neutral, the new awards program honors the people, organizations, and technologies delivering proven impact in industrial cybersecurity; winners to be announced live at the 2026 ICS Cybersecurity Conference in Nashville The post SecurityWeek Launches Critical Impact Awards to Recognize Excellence in Industrial Cybersecurity appeared first on SecurityWeek.

ICS/OTcritical infrastructureICS
SecurityWeekRead original
ExternalSoftware Engineering
DZone

Search Is Becoming the Control Plane for AI Agents

Your agent won't be able to discover tools in 5 years using hardcoded API integrations. It will look for the capability that it requires, read the description of the tool, and call it at runtime. That change alters the integration model altogether. Rather than developers having to wire in each and every OpenAPI spec to the codebase, agents will be able to discover, understand, and use capabilities from searchable tool catalogs on demand.

External
The Hacker News

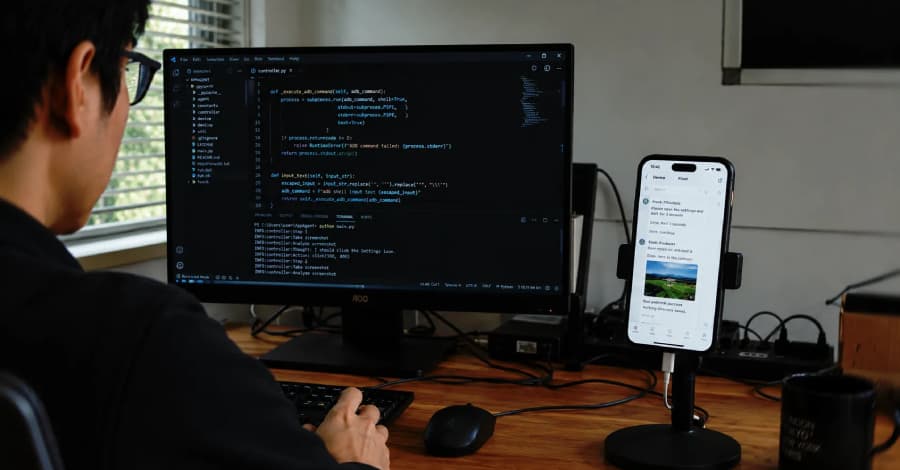
Open-Source Android AI Agents Could Let Invisible Screen Text Run Code on Host PCs

An Android app that can draw over other windows and write to shared storage can slip instructions to the AI agent driving that phone, in text no human eye will ever see. Two more steps, and the same app is running commands on the PC driving the agent. Researchers demonstrated that chain, plus six other attacks, against five open-source mobile agent frameworks: AppAgent, AppAgentX,

The Hacker NewsRead original
External
The Hacker News

N-day is Becoming N-Hour. Patching Faster Won't Save You.

Every patch is a confession. The moment a vendor ships a security fix, the diff between the old code and the new code tells anyone watching exactly what was broken and where. Turn that diff back into a working exploit, and you can hit every system that hasn't updated yet. This is N-day exploitation, and it's always been a race: the vendor patches, the clock starts, and defenders try to deploy

The Hacker NewsRead original
External
The Hacker News

New Bit2Watt Attack Could Let Cloud Tenants Disrupt Power Grids Without an Exploit

A cloud tenant using nothing but ordinary GPU access can push a data center's power draw up and down fast enough to threaten the grid it runs on, with no exploit and no break-in. That is the claim behind Bit2Watt, described by three Zhejiang University researchers in a paper accepted to CHES 2026, the IACR's hardware-security conference, and the evidence splits in two: they measured the power

The Hacker NewsRead original
ExternalCloud
Google Cloud Blog

Generosity Under Conditions: Hardening Google Cloud Access Management

In Google Cloud, Identity and Access Management (IAM) helps you maintain access control over your cloud resources and operations. While it includes other features, this is its primary purpose. If you ever tried to harden security over your application, you know the importance of the Principle of Least Privilege (PoLP) ‒ grant the absolute minimum permissions to your users and workloads to allow them to perform their tasks. You reach it through use of predefined roles and custom roles and setting

Developers & Practitioners
Google Cloud BlogRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.