ExternalAI
Hugging Face Blog
Real-Time Intelligence with IBM Time Series Models on Confluent
Hugging Face BlogRead original
Insights
Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.
From the engineering desk
Browse practical articles or follow the latest technology updates.
Subscribe via RSS →Curated links from external sources — not 360Softy original articles.
Comments
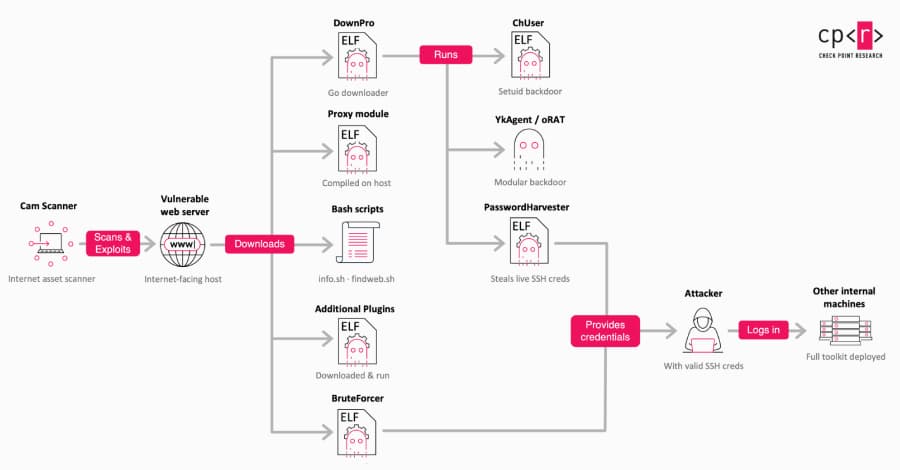
A Chinese-speaking cybercrime cluster known as Gambling Goblin has been observed installing malicious Apache modules on compromised web servers run by Brazilian government and educational institutions, and using them to divert visitors to attacker-controlled pages promoting online gambling and sports betting. Check Point Research said it has tracked the campaign since mid-2025. The modules
Comments
TL;DR Or, perhaps the problem isn't that AI has broken code review, maybe it’s that we've been using code review to solve the wrong problems I was on a panel recently with Brian Houck from DX at Code Remix, hosted by Moderne. It was one of the more interesting panels I’ve done, largely because we disagreed. As my colleague Martin Fowler says, panels are much more interesting when people disagree and both sides have a good argument. Brian and I definitely did. Brian has since written a thoughtfu
Article URL: https://lwn.net/Articles/1090585/ Comments URL: https://news.ycombinator.com/item?id=49535752 Points: 667 # Comments: 133
Virtualizor said hackers used a Border Gateway Protocol (BGP) hijack to divert Softaculous traffic. The hackers then used the diverted update traffic to deliver a malicious Virtualizor package to some installations. A hosting-provider account separately said 5 of its 34 checked Virtualizor hypervisors sustained root-level compromise. The incident window ran from approximately August 28 at 20:57
Let’s start with a conversation
An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.
Prefer email? [email protected]